
Teaching notes
Short, practical notes on running hands-on digital forensics and incident response labs and exams that stay honest.
Analyze a disk image in Autopsy: a beginner's walkthrough
Open a disk image in Autopsy, run the right ingest modules, and find the artifacts that answer the question. A walkthrough for students new to DFIR.
Read the post →
GCFE practice: a different Windows forensics case for every student
Registry, prefetch, USB history and event logs: one authored case becomes a per-student Windows box with a verified answer key.
What to look for in a digital forensics lab platform: a buyer's guide
Seven questions to ask before you buy a DFIR training platform: realistic evidence, a trustworthy answer key, anti-cheating, LMS grading, offline operation, cert alignment, and total cost at your size.
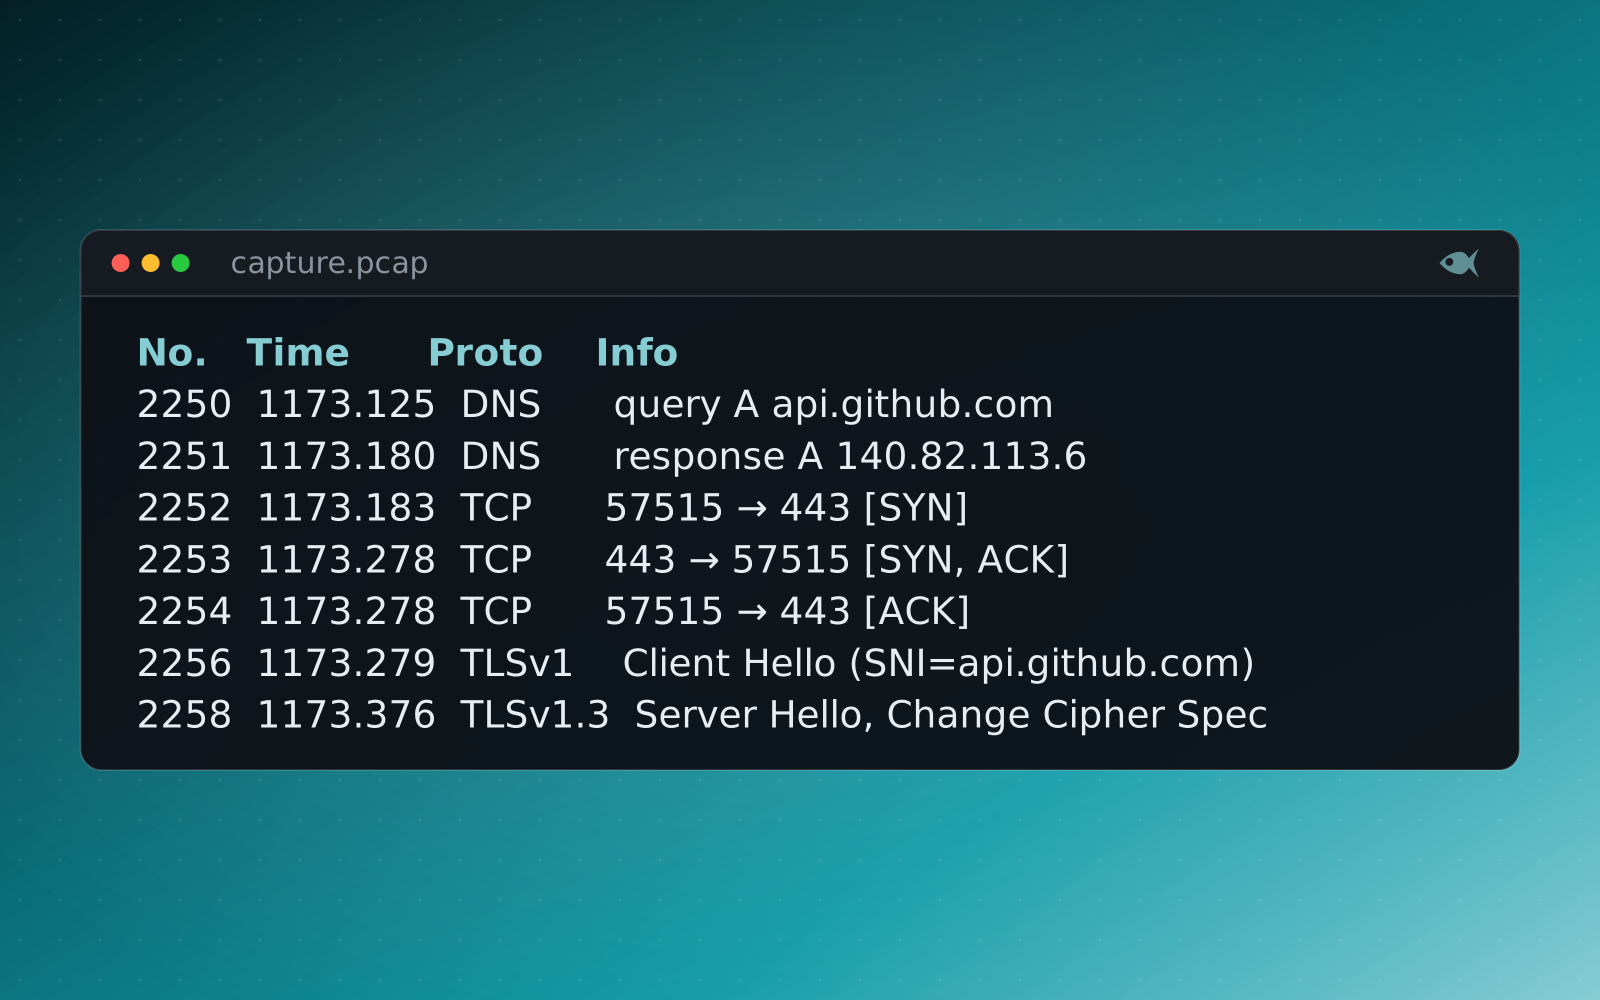
Spotting C2 beaconing in a packet capture
Teach students to read a PCAP by timing (interval, jitter and payload), follow the stream, and tell the beacon from benign noise.
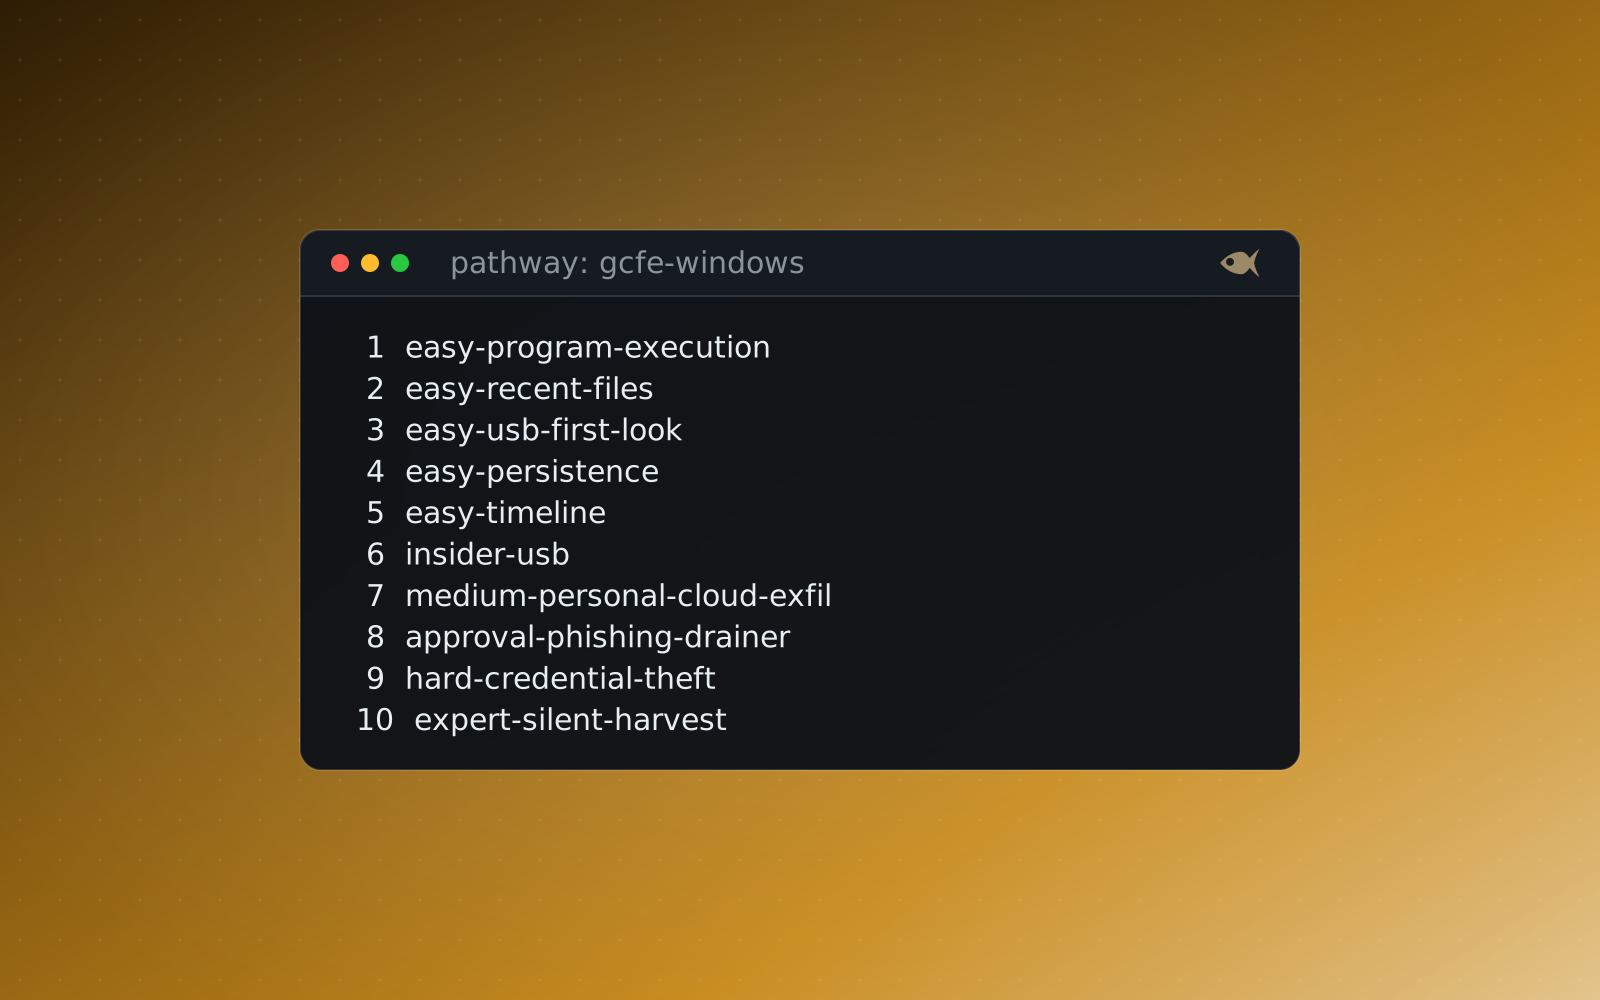
From first look to capstone: building a DFIR learning pathway
Sequence a course from a First Look on-ramp up the difficulty ladder to a cert-prep capstone, with guided mode easing beginners in.
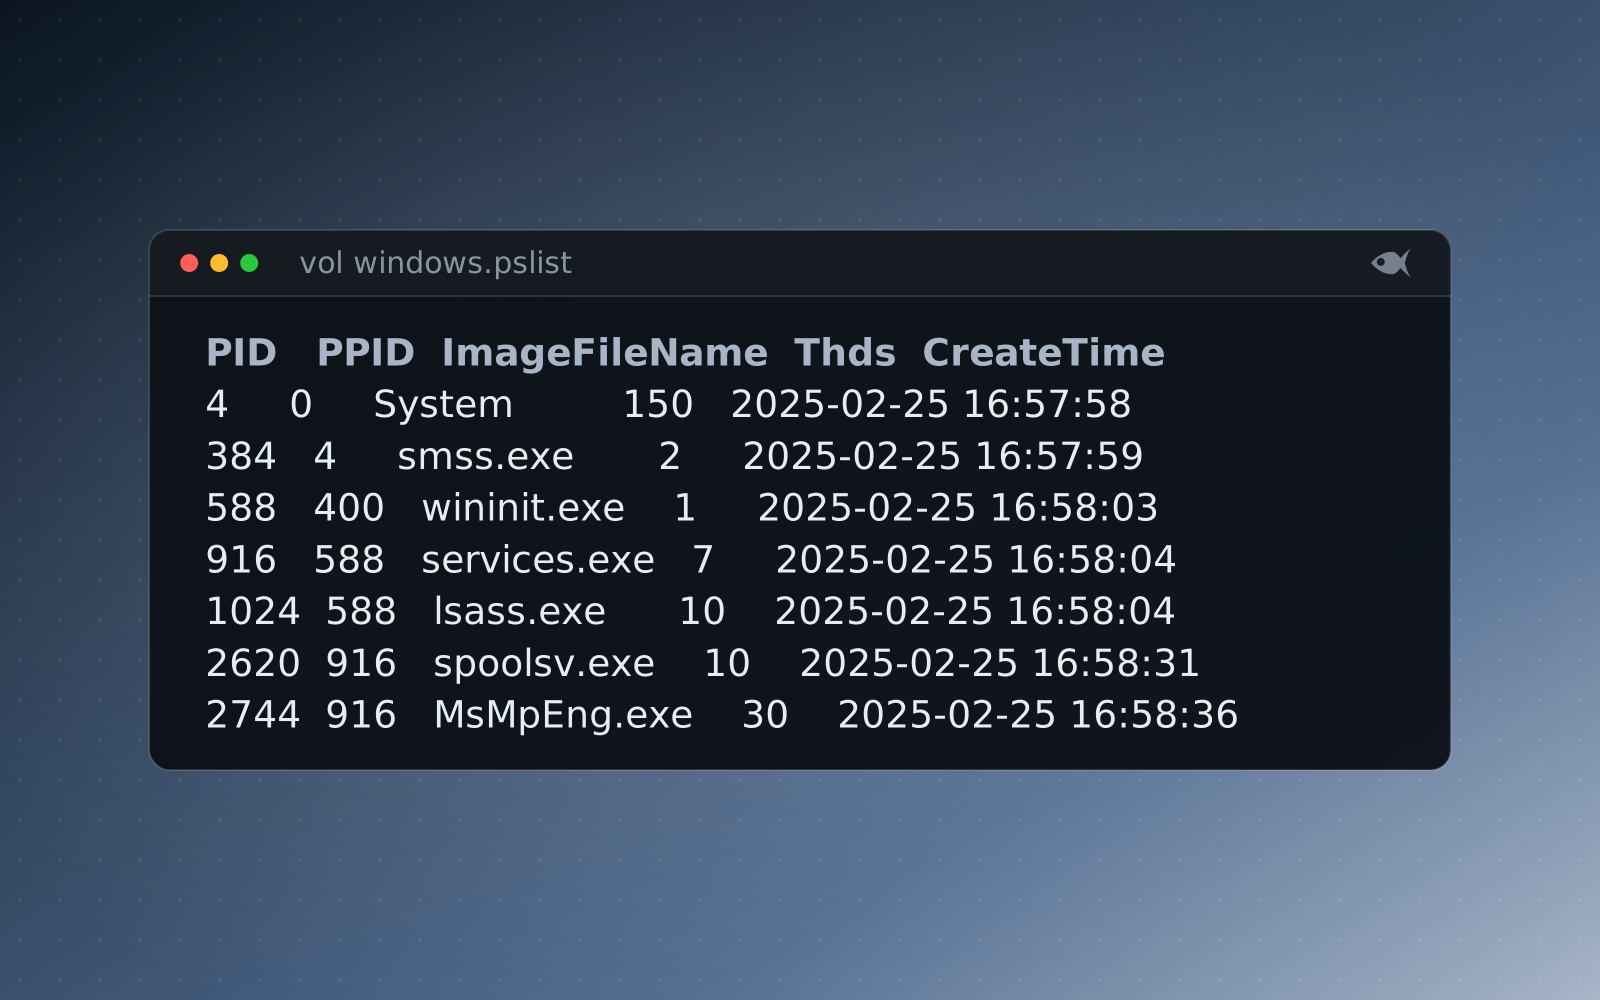
Getting started with memory forensics in Volatility 3
Install Volatility 3, list processes, follow them to network connections and command lines, and spot injected code in a memory image.
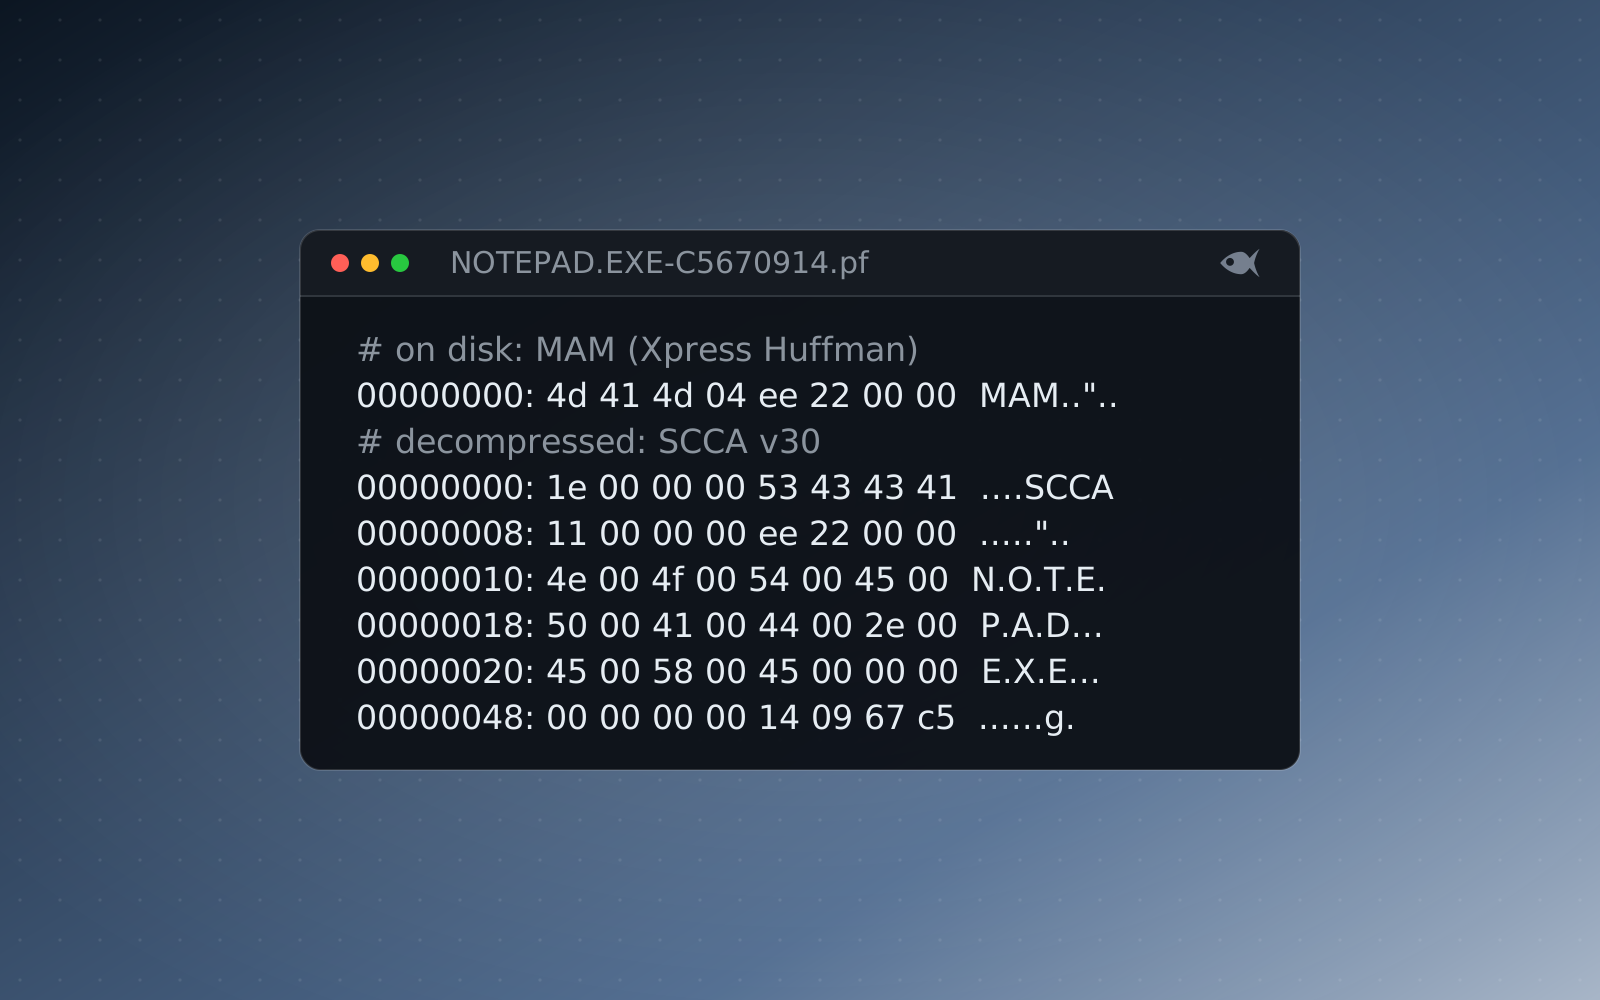
Windows Prefetch forensics: a PECmd walkthrough
What a Prefetch file records, how to parse the folder to CSV with PECmd, and the misreads that cost marks: first run vs file creation, disabled Prefetch, the hash in the filename.
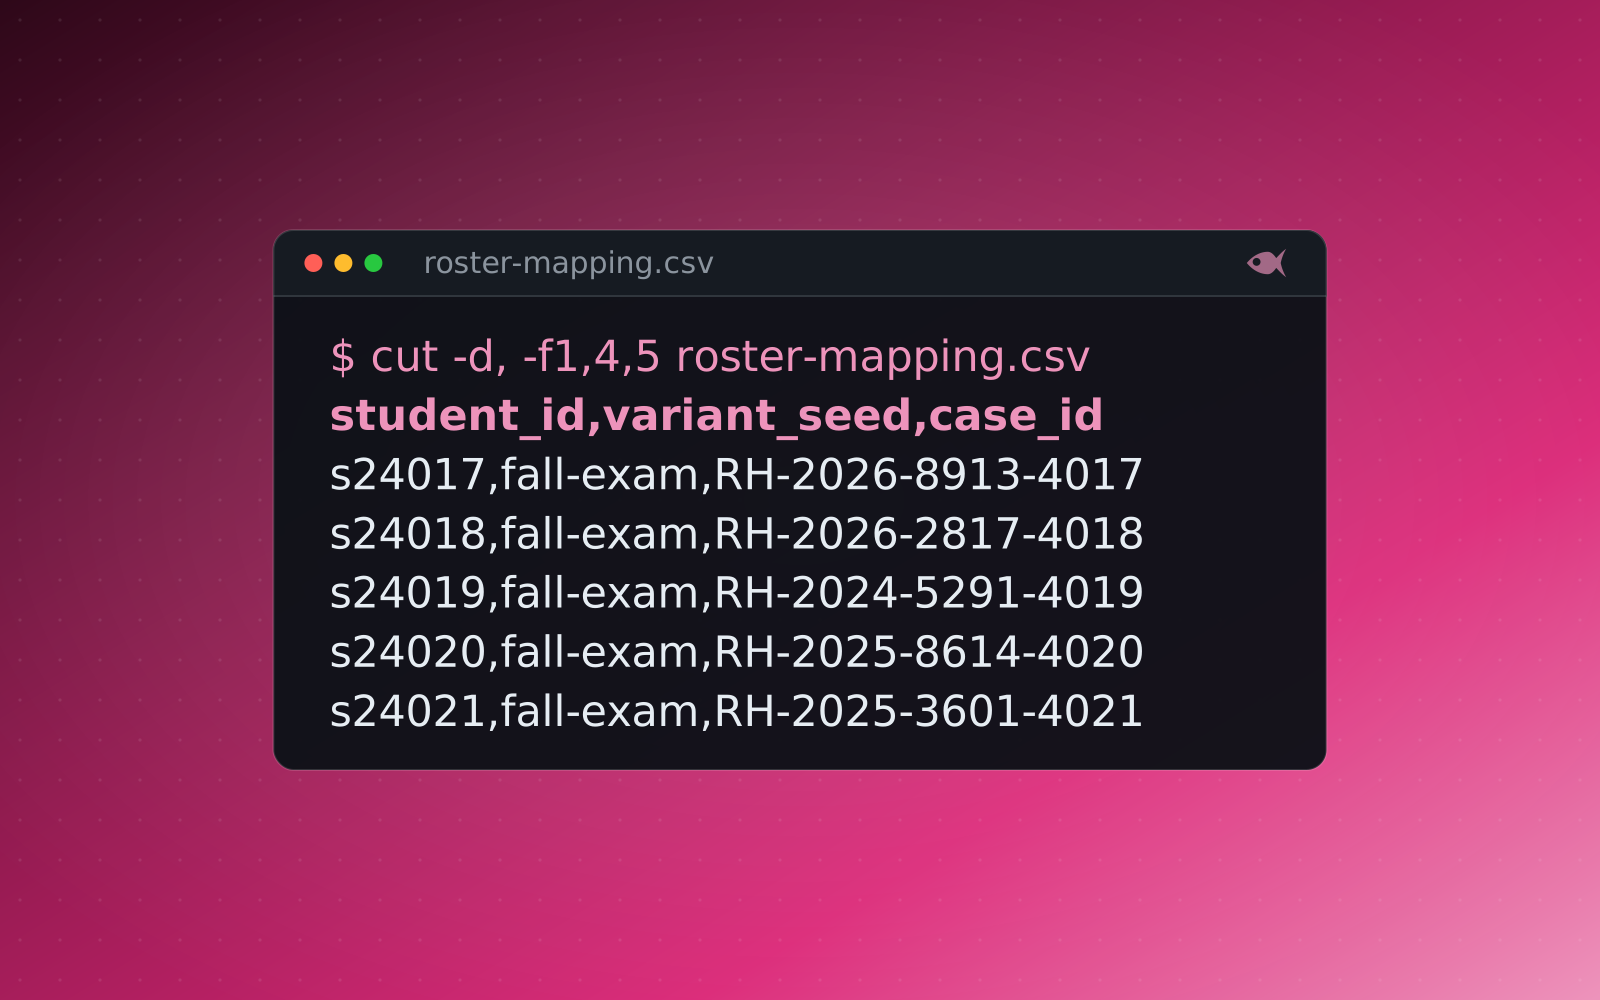
Run a forensics exam students can't copy
Why shared evidence makes copying inevitable, and how per-student cases, an in-browser solve portal and LMS grade passback fix it.
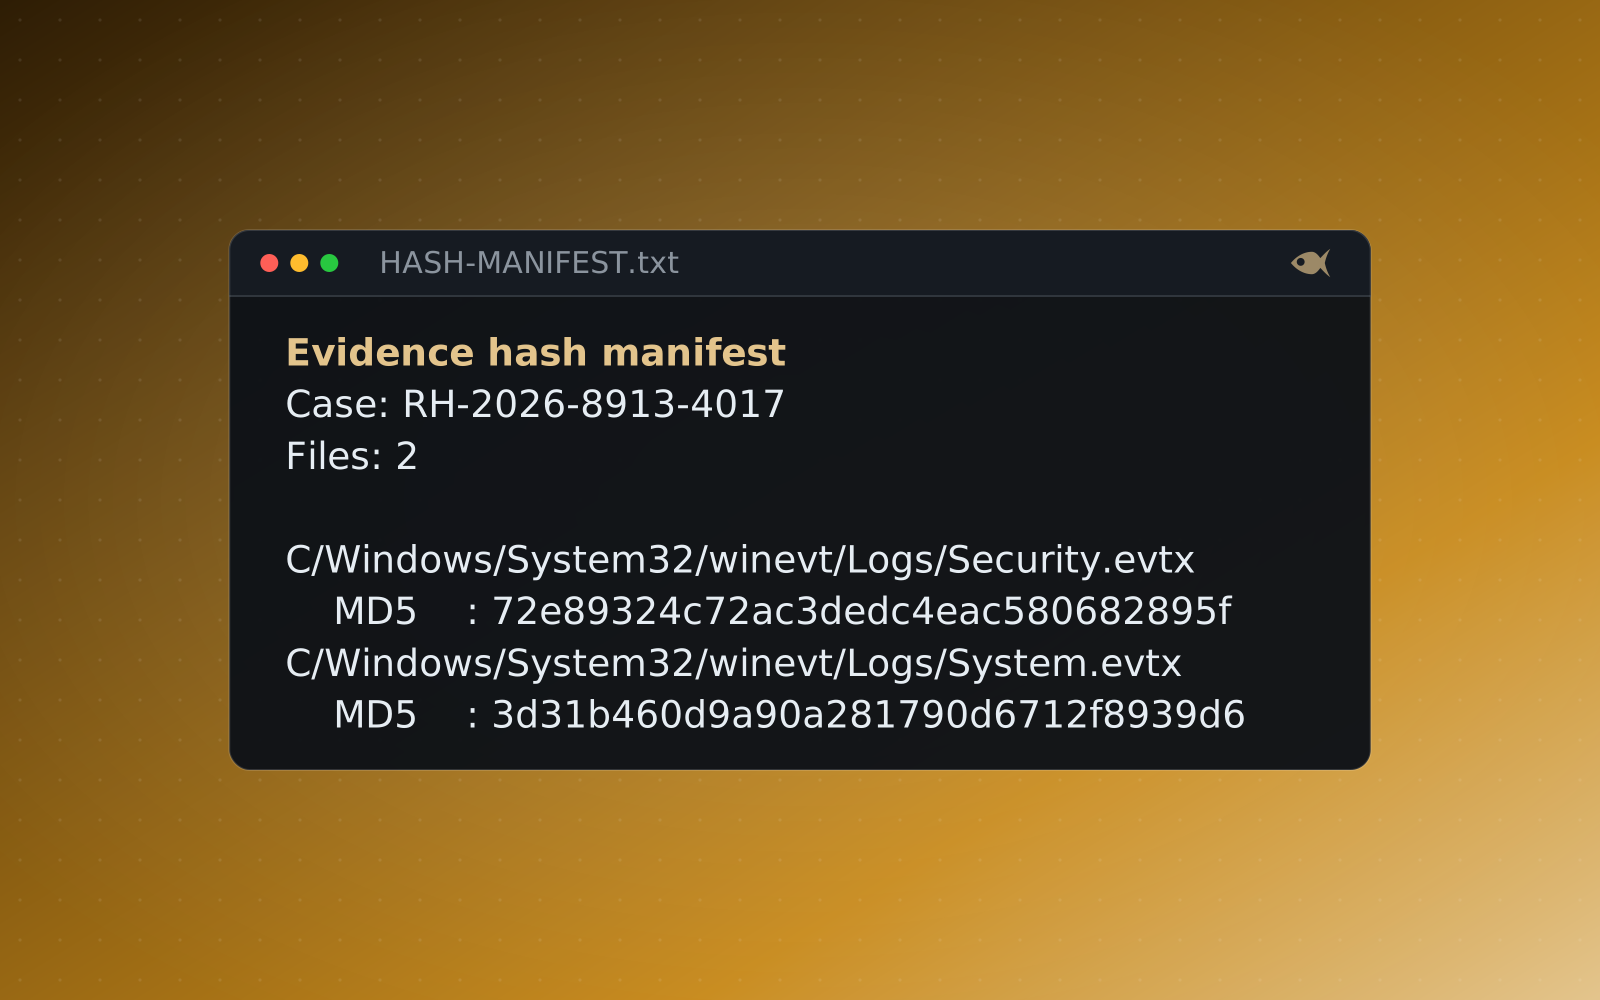
Teaching chain of custody in the forensics classroom
Make custody a habit from the first lab: the fields that matter, hashing on receipt as the first row, how to grade the form, and the mistakes students make every term.
How to grade a digital forensics lab fairly
Tolerate hash case, time zones and whitespace, give parts credit for parts, keep a human on the prose, show the reason on every score, and make a copied answer a wrong one.
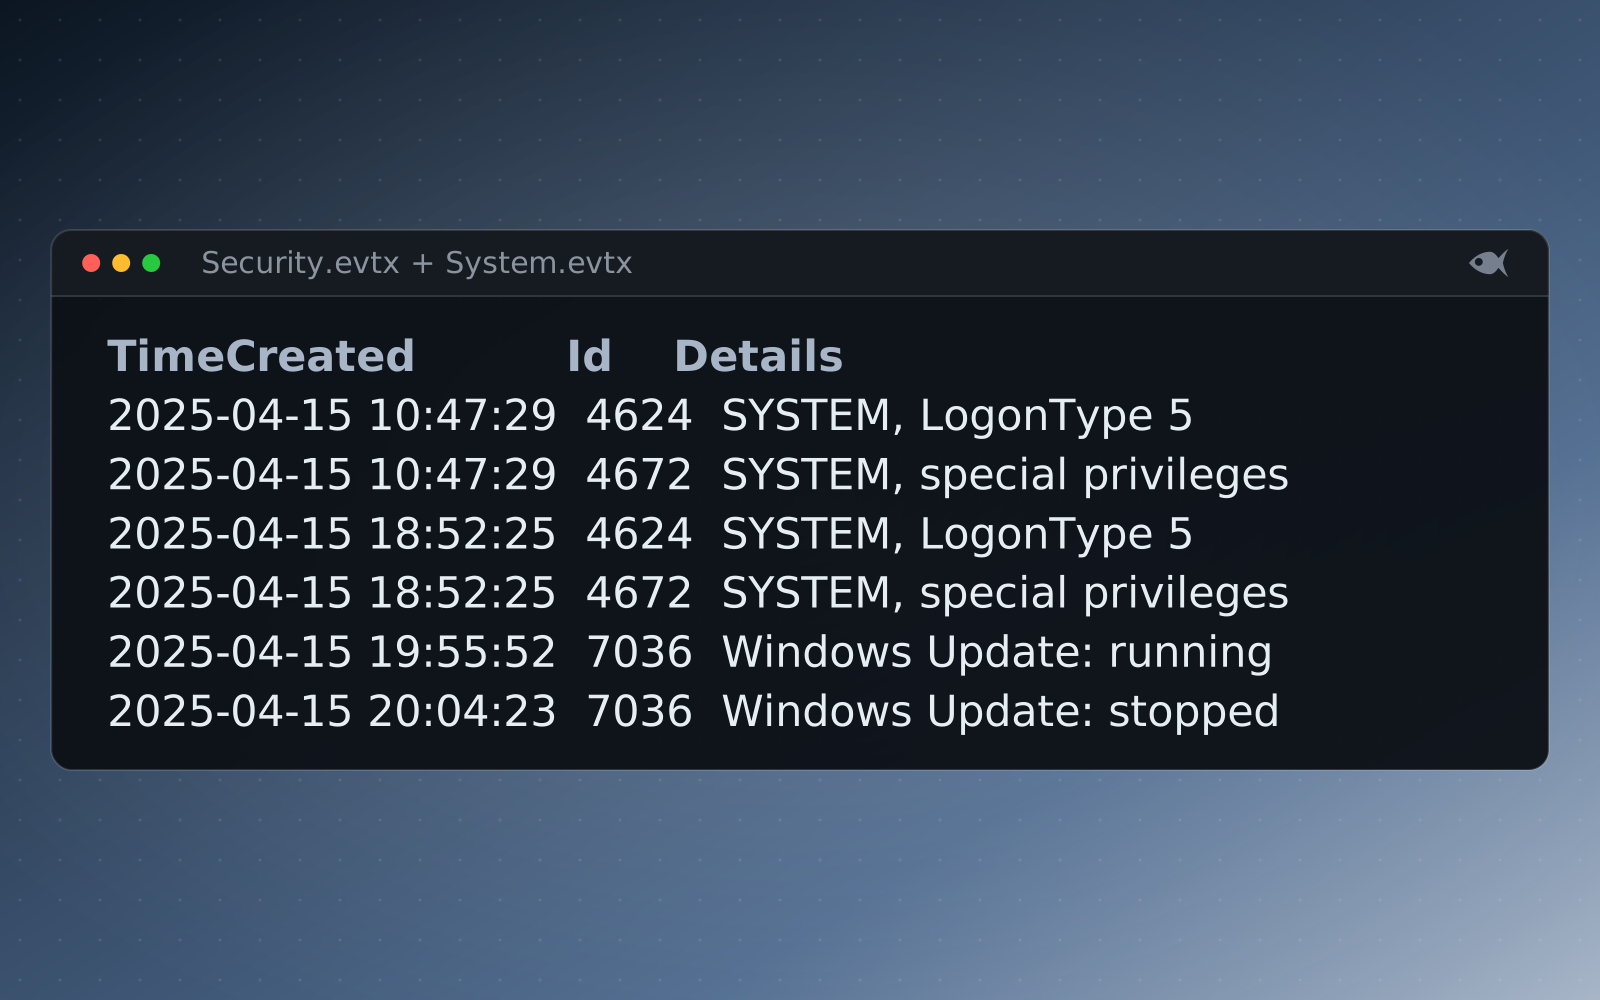
Turn Windows event logs into a timeline with EvtxECmd
Parse Windows .evtx logs into a clean CSV with EvtxECmd, open them in Timeline Explorer, and read the Event IDs that matter.
How to run a SOC analyst onboarding program with hands-on labs
New analysts learn the queue by working it. Give each hire their own graded EDR and SIEM incidents, ramp from a first alert to a scoped intrusion, and measure readiness instead of guessing it.
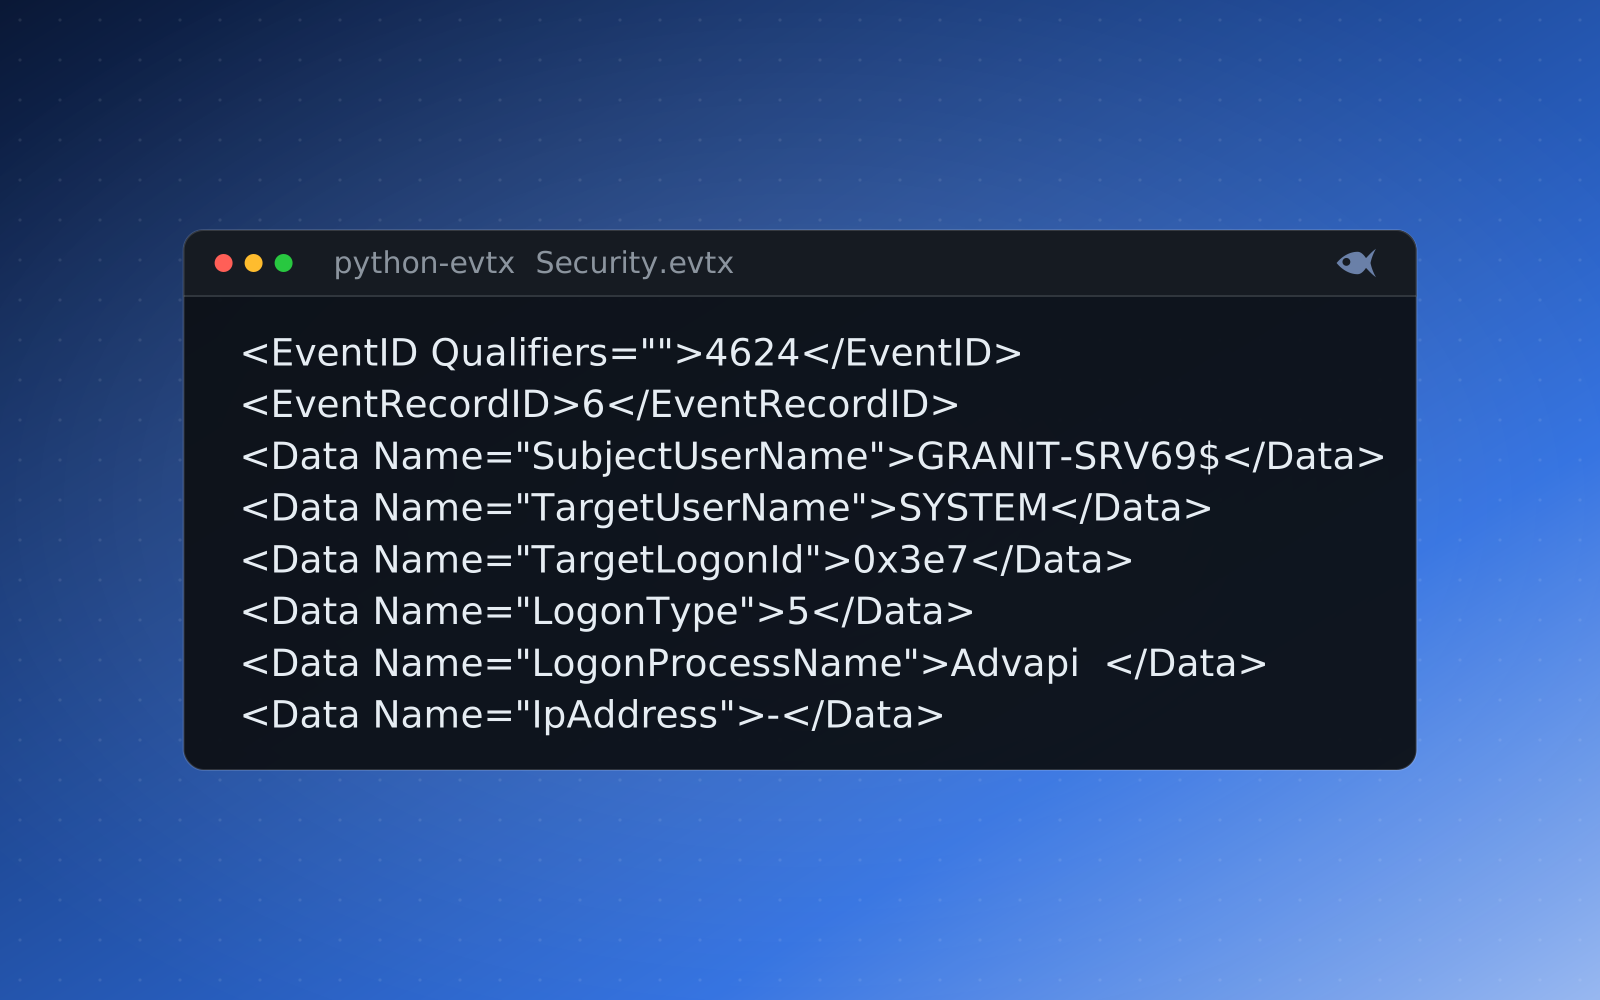
Detecting lateral movement in Windows event logs: the 4624 to 4688 pivot
Match a remote logon to the processes it spawned by logon session, read subject against target correctly, and trace an attacker host to host.
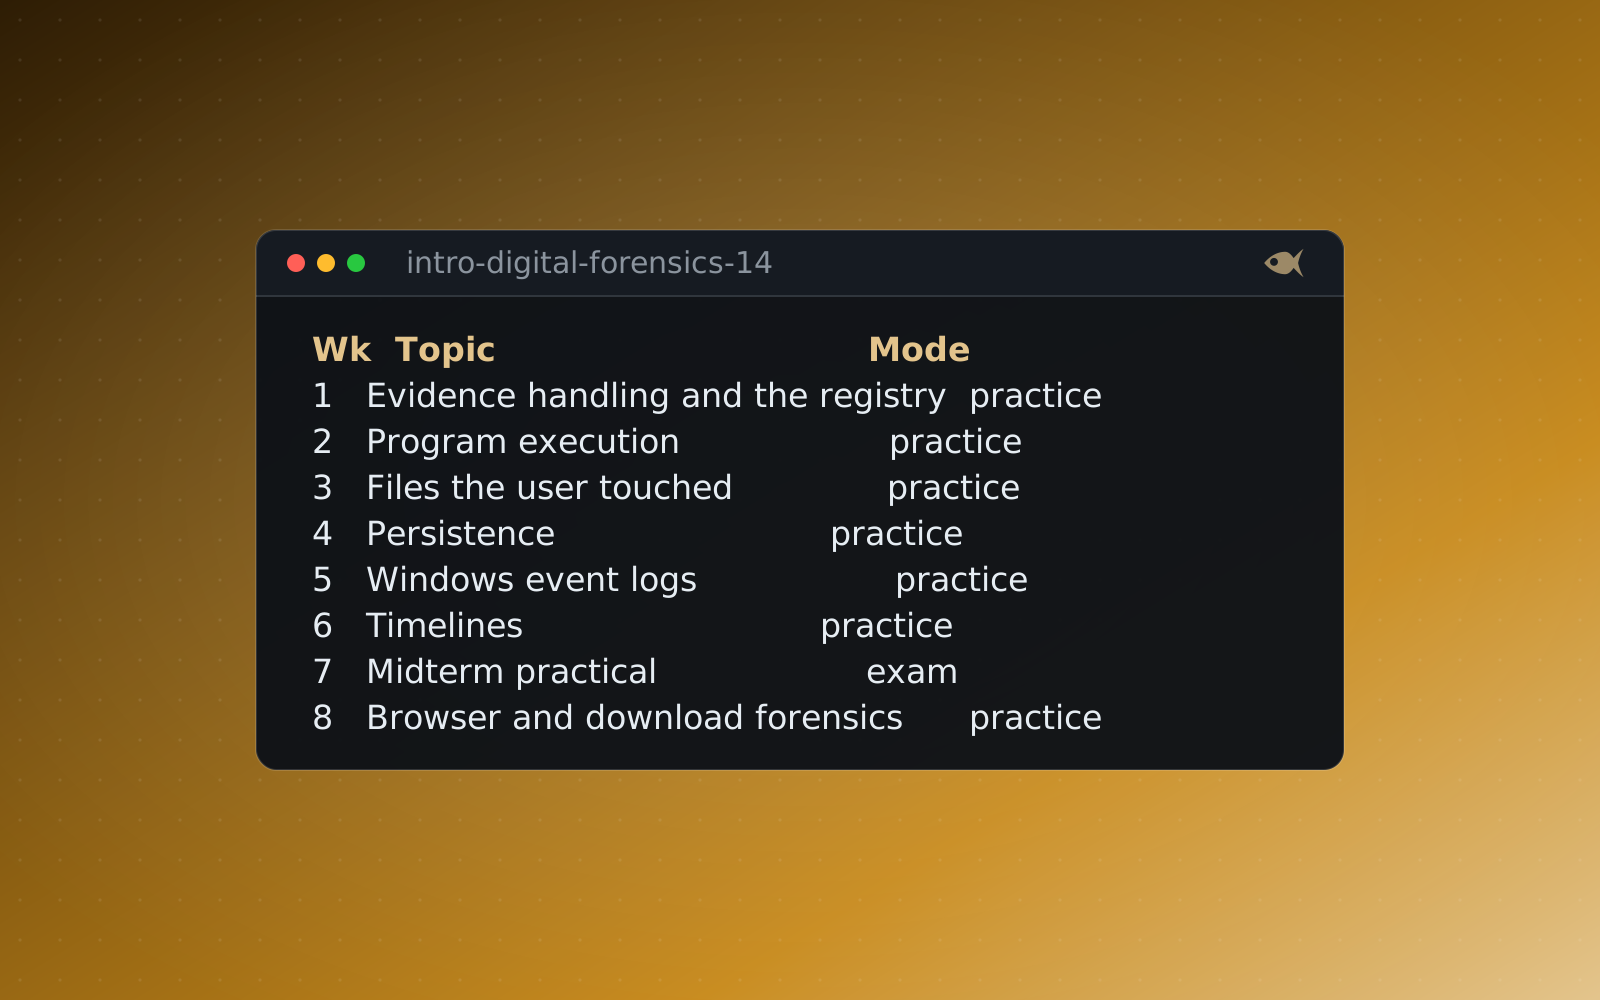
How to build a digital forensics course syllabus
The week-by-week logic from a single-artifact First Look to a multi-artifact capstone, why memory and network come late, the assessment mix, and what to do in week one.
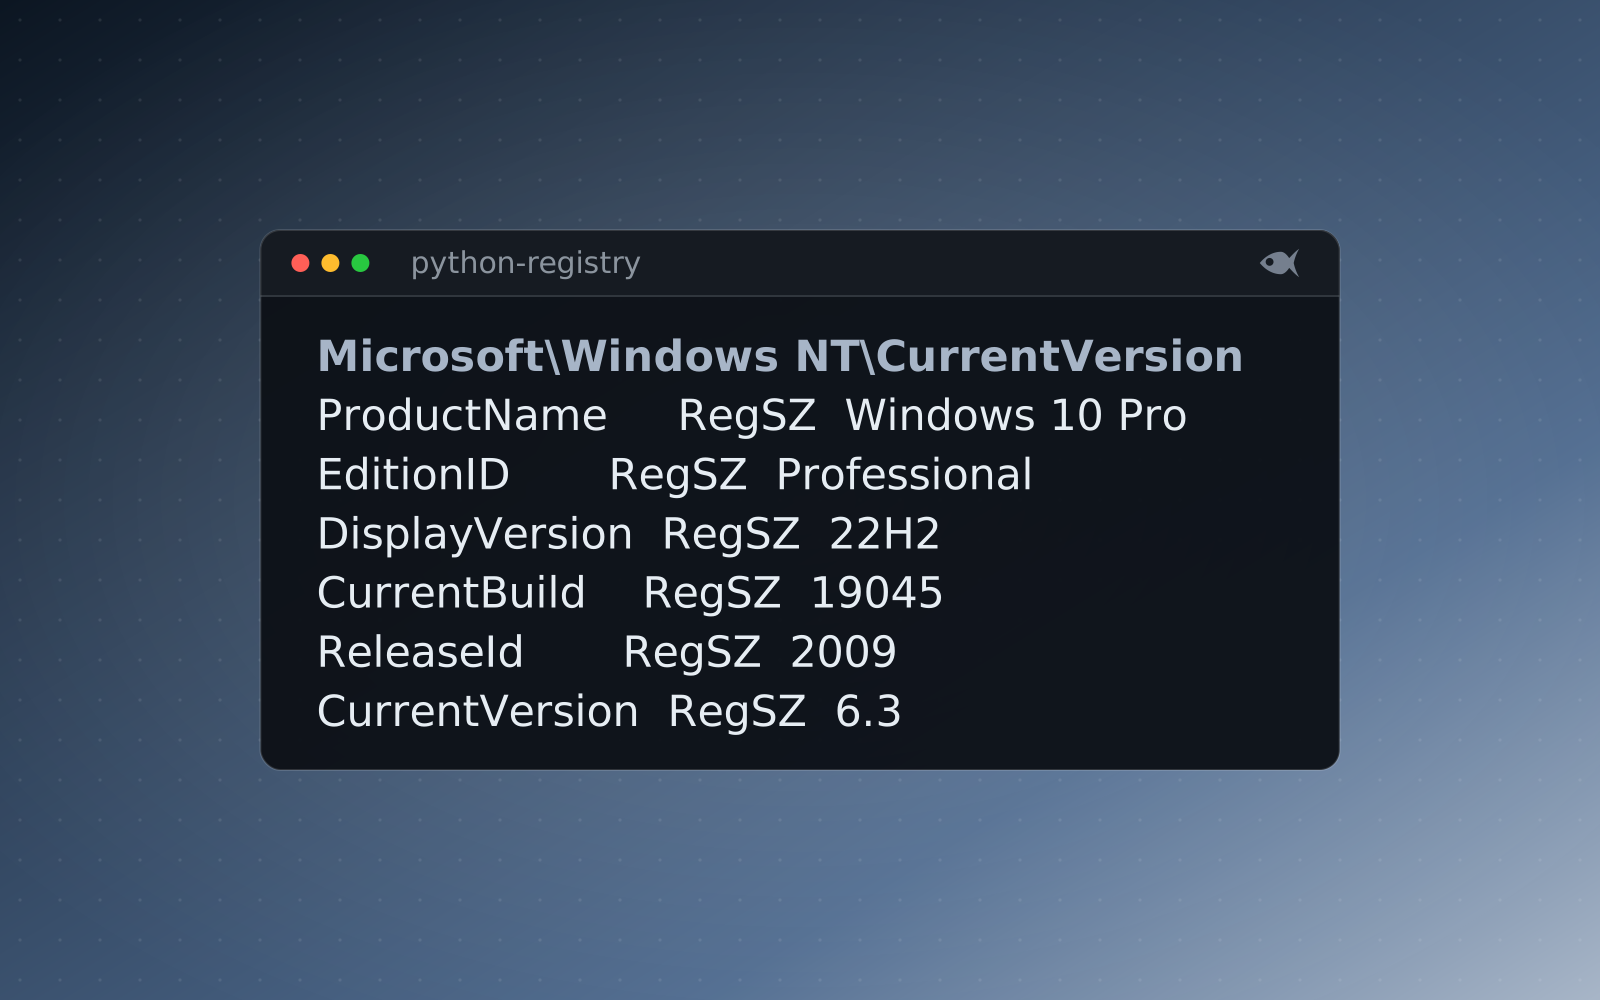
Read the Windows registry with Registry Explorer
Load a hive in Registry Explorer, use the forensic bookmarks, and read the keys that show USB use, program execution and persistence.
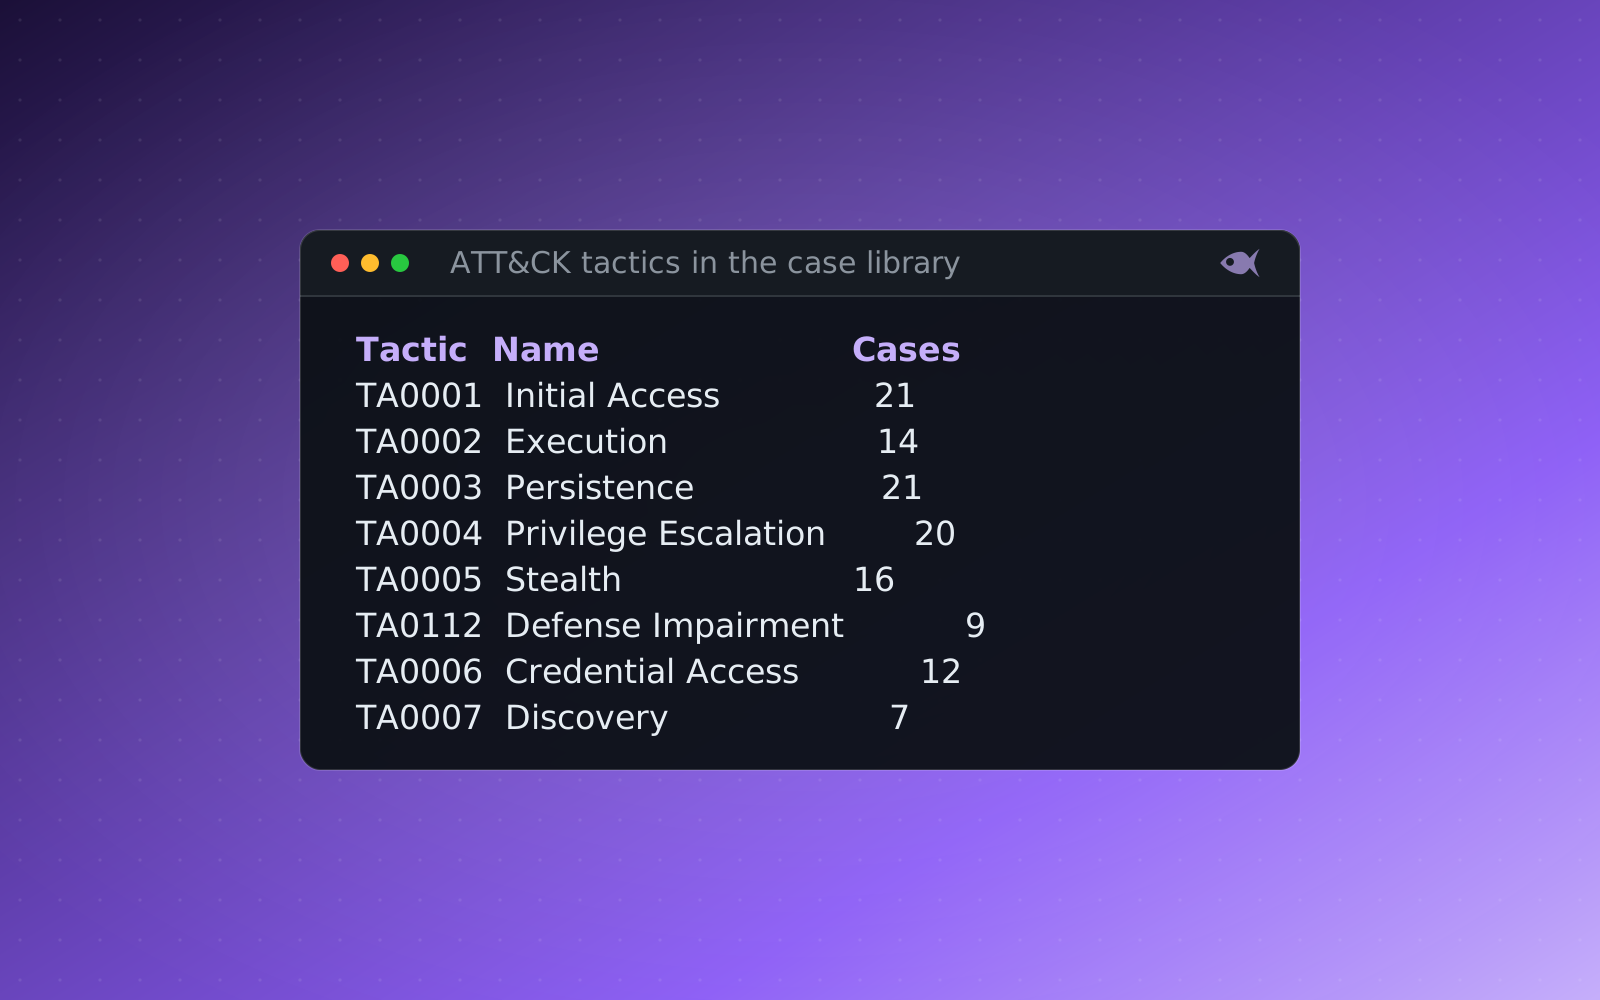
Teach MITRE ATT&CK with hands-on labs, not slides
ATT&CK-tagged cases make a technique something you find in the evidence and detect, not a cell to memorize on a chart.
Wireshark for beginners: packet capture basics
Fix the clock, write display filters, read Conversations before packets, follow the stream, export objects, learn the DNS and HTTP columns, and save a filtered subset.
Hands-on forensics training in an air-gapped facility: no cloud, no account, no egress
A cyber range needs the internet. Red Herrings generates every case on the analyst's own machine, activates offline, and never sends student work anywhere, so training runs inside a secure facility.
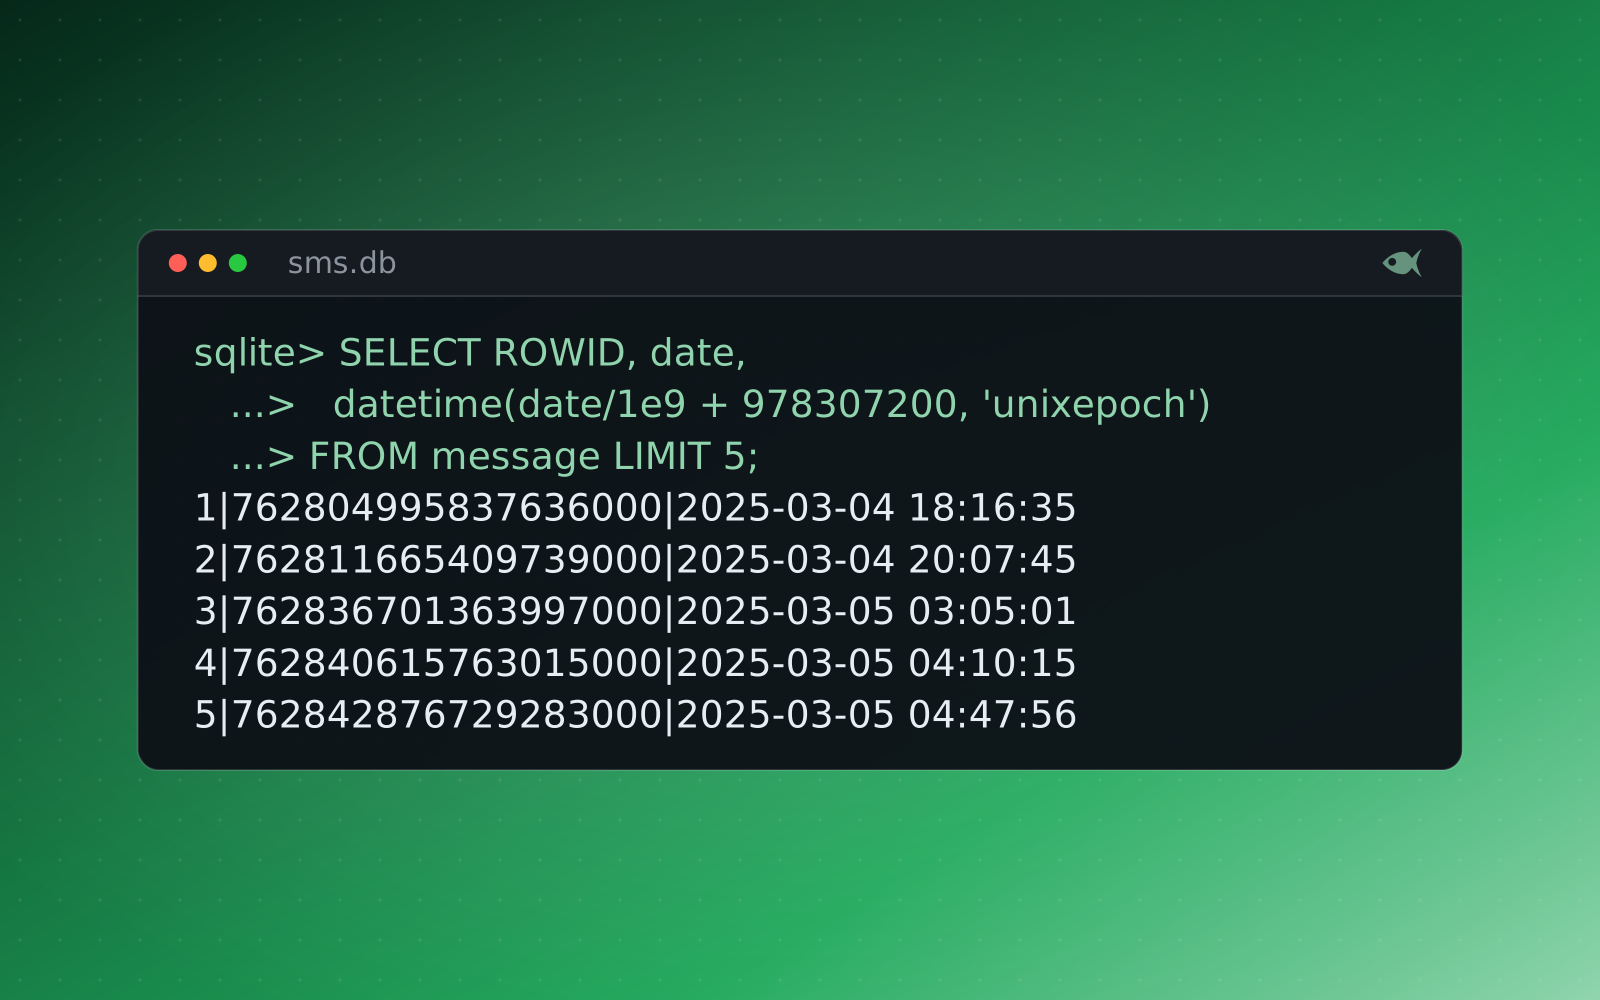
Reading an iPhone sms.db: the iMessage joins and the Cocoa-time trap
Join message, handle, chat and chat_message_join into a real thread, then decode Apple Cocoa time (nanoseconds since 2001) the way that trips students up.
White-label DFIR training: author and resell your own cases
Run the whole platform under your own brand, write cases in the visual editor, and resell them as packs. One Pro license, unlimited participants, nothing to host.
Build a blue-team CTF your analysts can't Google the answers to
A shared CTF leaks the moment the first team solves it. Per-seed cases give every analyst their own flags, computed from their own evidence, so the only path to an answer is through the work.
Run an incident response exercise from real EDR and SIEM evidence
Work an IR case from the responder's own tooling, mapped to MITRE ATT&CK and the NIST 800-61 phases, with time pressure built in.
What's new: an account portal, certificates, and dozens more cases
A self-serve account portal, printable certificates and badges, student and veteran pricing, and a library now dozens of cases strong across digital forensics and incident response.
Cyber range vs generated cases: what actually fits a training budget
A cyber range rents you one shared cloud lab by the seat. Generated cases give every learner their own, run on hardware you already have, and cost the same for ten learners or a hundred.
Incident response tabletop vs. hands-on exercise: what each measures
A tabletop measures decisions and communication; a hands-on exercise on EDR and SIEM evidence measures analysis and the containment call. How to run both in a term and score each.
No posts in this category yet.